Architecture
The site has no server. Every page is a file in one S3 bucket. CloudFront is the only service allowed to read that bucket, and it is the only public entry point.
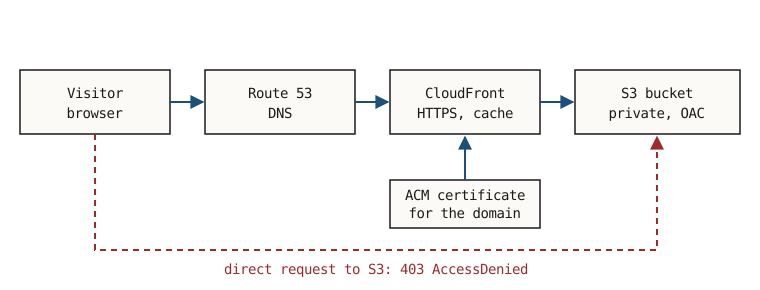
Services and their jobs
- Amazon S3
- Storage for the website files: HTML, CSS, JavaScript, and images. The bucket stays private.
- Amazon CloudFront
- The content delivery network. It is the public entry point. It serves HTTPS and redirects HTTP to HTTPS.
- Origin Access Control (OAC)
- A CloudFront setting. CloudFront signs its requests to S3, and the bucket accepts only those signed requests.
- AWS Certificate Manager (ACM)
- Issues the TLS certificate for csce412zhangdavid275.store. CloudFront uses it to serve HTTPS.
- Amazon Route 53
- DNS. It answers the question "where is csce412zhangdavid275.store?" with the CloudFront address.
Request path, step by step
- The browser asks DNS for csce412zhangdavid275.store. Route 53 answers with CloudFront.
- The browser opens an HTTPS connection to CloudFront. CloudFront presents the ACM certificate.
- A request that arrived over plain HTTP gets a redirect to the HTTPS address.
- CloudFront reads the file from the S3 bucket with a signed request. The bucket accepts it because of OAC.
- CloudFront returns the file to the browser and keeps a copy for later visitors.